How RFID Cuts Gray-Market Diversion: From Scan to Alerts
Counterfeiting gets the headlines, but the quieter leak in most distribution networks is diversion: genuine product, sold outside its authorized territory or channel. It does not show up as a fake-goods raid; it shows up as flat regional sales, angry authorized dealers, and discount listings that undercut your own price list. Closing it is a data problem before it is a technology problem — and supply chain traceability anti counterfeiting infrastructure, once deployed for authenticity, already contains the sensors you need to solve it. This article explains the scan-to-alert loop: which checkpoints produce evidence, which alert rules catch diversion, and what published deployments actually report.
Diversion control starts with item-level identity: without unique serials, there is nothing to trace and nothing to compare.
Diversion Is Not Counterfeiting — and the Fix Is Different
Two problems, two mechanisms. A counterfeit is a product that was never made by you. Diversion (gray market, channel leakage, cross-territory selling) is your own authentic product sold where it should not be — by a distributor clearing excess stock, by a wholesaler serving a region it is not authorized for, or by an insider leaking allocation. Authentication tells you whether a product is real. Diversion control needs one more thing: a record of where each item has been, and where it is allowed to be. RFID and encrypted NFC labels, deployed for anti-counterfeiting, produce exactly that movement trail as a by-product.
What Published Deployments Report
Every figure below comes from a published source, not from our client work. Treat them as reported magnitudes that show the mechanism works — not as a forecast for your network.
| Reported case | Result | Source type |
|---|---|---|
| Baijiu brand using RFID/NFC chips plus blockchain traceability with smart-contract diversion alerts | Channel diversion down ~70% | Official Chinese government solution listing (Fujian Development and Reform Commission, Chinese-language) |
| Multinational beauty group rolling out transfer-evident RFID labels across fragrance and color cosmetics, with authorized-territory matching per TID | Diversion activity down 76% over 12 months | Vendor/trade report (Chinese-language industry press) |
| Premium boutique forensic audit: distributor "back-door diversion" into discount channels | Revealed 35% of potential revenue leaking; leak traced to two distributors | Published case study by a security integrator |
| Appliance manufacturer using RFID supply chain visibility for channel auditing | Gray-market incidents down over 60% within one year | Vendor case report |
| Cosmetics brands adopting RFID anti-counterfeiting (2025 trade survey) | Channel complaint rates down 72% | Industry survey, Chinese-language packaging trade press |
One planning rule from the same trade reporting is worth carrying into your budget conversation: the economics tend to turn positive when annual losses from fakes and diversion exceed roughly three times the total label cost. For most mid-size brands, diversion losses are simply not measured — which is the first thing to fix.
The Scan-to-Alert Loop: Four Checkpoints
Traceability is not a database you upload once; it is a loop that closes every time an item is read. Four checkpoints cover the vast majority of real diversion patterns:
- Encoding (factory). Each unit gets a unique serial bound to SKU, batch, production date and authorized market. This is where 100% read-verification matters — an unverified batch is an untraceable batch.
- Shipment out (brand warehouse). Fixed readers or handheld scans at dispatch register which distributor received which serials. This is the reference point for every later comparison.
- Receipt in (distributor, regional warehouse, store). Inbound scanning confirms the shipment arrived at the authorized node. Gaps here are the first warning: goods left, but never arrived where they were sent.
- Consumer tap (market). NFC or QR verification from the end buyer is the strongest evidence available: a serial authorized for one province being scanned repeatedly in another is direct proof of diversion, with a timestamp and a location attached.
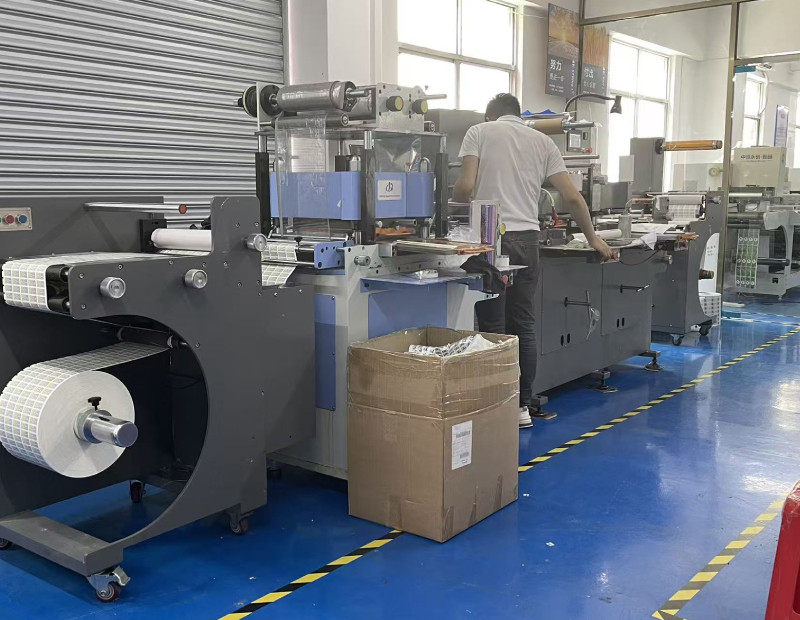
Identity is created on the line: serials written at encoding and 100% read-verified are the reference against which every later scan is compared.
The Five Alert Rules That Actually Catch Diversion
Data alone changes nothing; the value is in rules that fire on anomalies. These five cover most diversion patterns we see in traceability projects:
| Signal | What it indicates | Typical action |
|---|---|---|
| Out-of-territory consumer scans | Authorized for market A, scanned in market B — repeated scans confirm a live gray market, not a traveller | Trace back through the last recorded checkpoint to the responsible distributor |
| Scan-out / scan-in mismatch | Serials dispatched but never receipted at the destination node | Exception report to channel ops; require receipt scanning as a contract condition |
| "Ghost inventory" | Warehouse system shows healthy stock while regional sales stay flat — classic signature of back-door diversion | Forensic scan audit on site; reconcile physical vs system stock |
| Duplicate or reused serials | Same identity appears in two places, or a consumed identity reappears — recycled labels and re-marked returns | Quarantine the batch, investigate the label supplier and the return process |
| Bulk-scan velocity | Hundreds of verification taps from one device or one location in minutes | Flag as an audit or scraping pattern; rate-limit and review |
From Alert to Evidence You Can Act On
An alert that cannot be defended in a distributor meeting, or in arbitration, is not worth much. The traceability log should produce, for every incident: the serial range, each timestamped checkpoint event with reader or device identity, the scan location, and the deviation from the authorized territory matrix.
Consumer taps are the market-facing sensor: an authorized serial scanned repeatedly outside its territory is direct, timestamped diversion evidence.
That package is what turns a suspicion into a documented contract breach. Pair it before launch with the paperwork that makes enforcement possible: territory definitions in the distribution agreement, receipt-scanning obligations, audit rights, and penalty clauses. Technology without contract terms produces interesting charts and no behaviour change. The same holds for the authenticity side of supply chain traceability anti counterfeiting: the evidence trail is only as strong as the contractual right to act on it.
How It Maps to Our Stack
In our deployments the layers are deliberately split: UHF RFID handles case and pallet movement at warehouse doors and distributor docks, where bulk reading at distance is the requirement; encrypted NFC (NTAG 424 DNA class) handles item-level verification in the market, where each tap must be provably fresh and non-copyable — the cryptographic mechanics are explained in our NTAG 424 DNA authentication deep dive. The frequency and chip decision that precedes both is covered in the RFID label analysis, and the size of the underlying fake-trade problem — context for why channel integrity programs get funded — is in our 2026 statistics summary.
Honest Boundaries
- Reported figures are not your figures. The percentages above come from other organisations' published cases. Our own programs start with a pilot and agreed KPIs, and we publish no client data.
- Alert precision needs tuning. A first version of any territory rule will flag travellers, resellers and returns. Budget 4–8 weeks of rule calibration against real scan data before judging results.
- Diversion control is commercial, not just technical. If your distribution contracts do not define territories and receipt obligations, technology alone will not close the leak.
- Consumer scans are a sample, not a census. Tap rates vary by category; checkpoint scans at logistics nodes carry the load, consumer taps supply the proof.
See the Demo
Bring a product and a channel problem. We will walk your team through the scan-to-alert flow on a live dashboard: encoding, checkpoint reads, territory rules, alert generation and the evidence package. See the demo — or start with an encoded sample batch on your own SKU.